C
Claude
Anthropic's AI assistant
Add Authdog authentication to my Next.js app...


Authentication
Social, passwordless, MFA, and enterprise SSO.
Hosted screens
Every screen below is live. Host it on your domain, drop it in as a component, or call the same APIs behind a screen you already built.
A complete sign-up flow with the methods you enabled, validation, and verification built in.
Learn more about <SignUp />Social providers, passwordless, MFA challenges, and enterprise routing handled on one screen.
Learn more about <SignIn />One-tap sign-in from the inbox. No password to remember, nothing to rotate.
Learn more about <MagicLink />TOTP, SMS, and email step-up, shown only when the policy asks for it.
Learn more about <MfaChallenge />Self-service profile, security settings, connected accounts, and sessions.
Learn more about <UserProfile />Social SSO
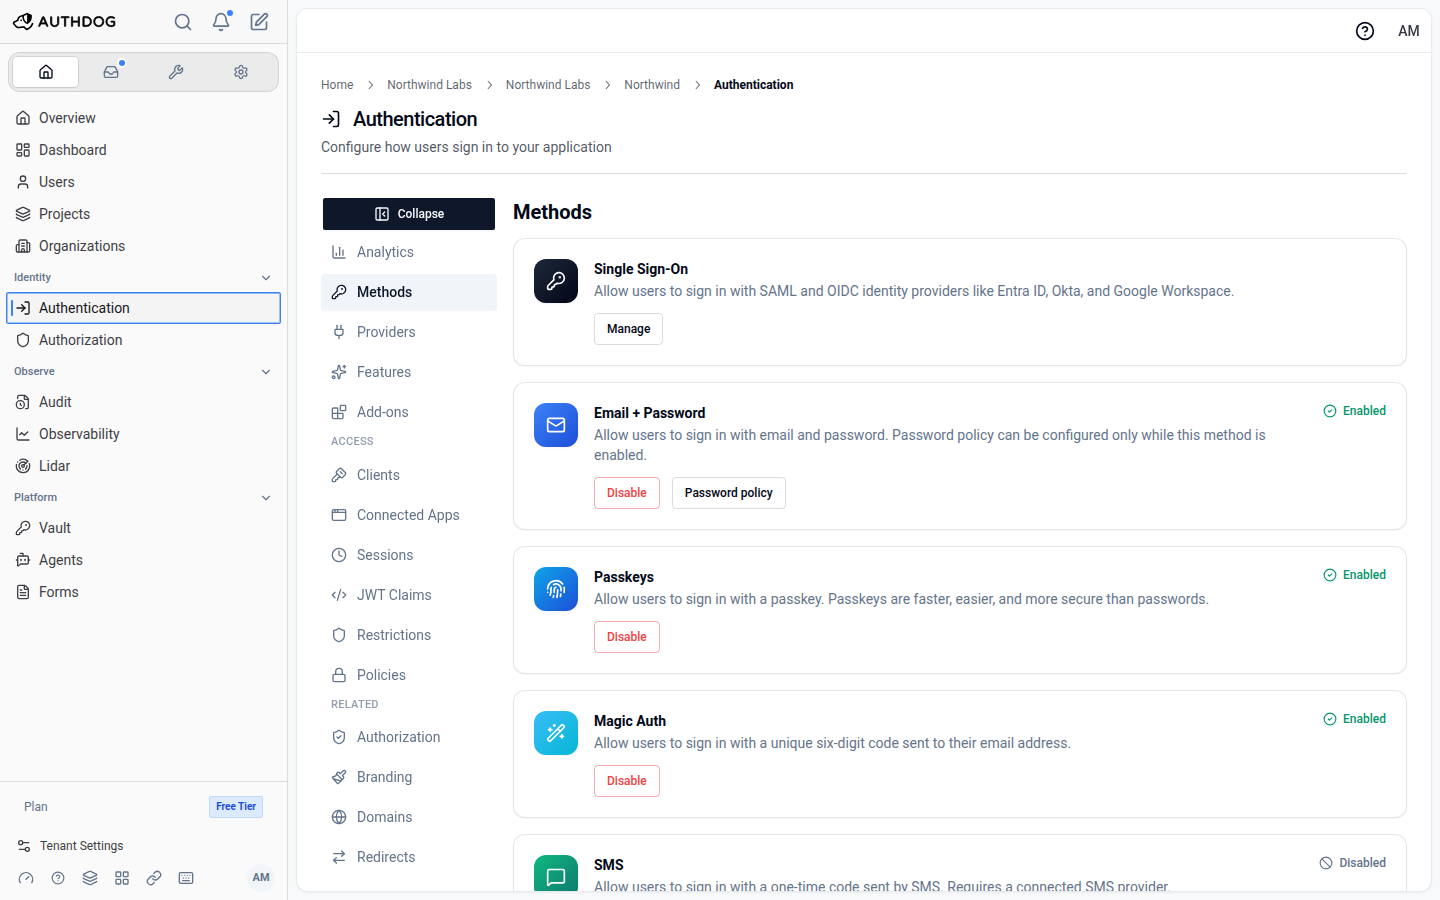
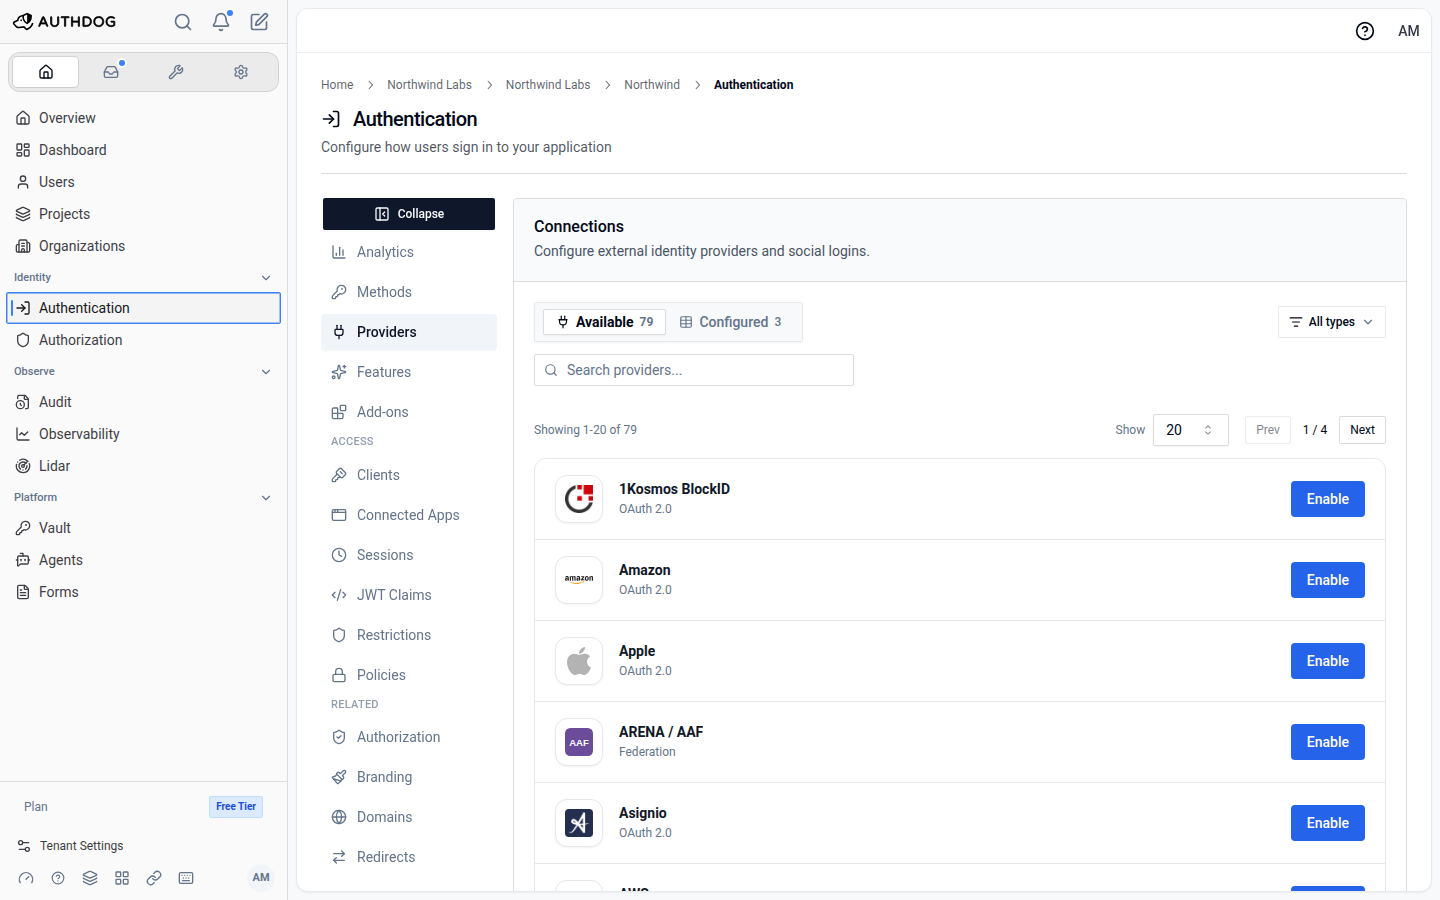
Google, GitHub, Microsoft, Apple, and the rest. Turn them on per environment. Duplicate accounts get linked, not created.
Connect Google, GitHub, Microsoft, Apple, and more from the console, with no provider-specific code in your app.
Users who sign in with a second provider land on the same account instead of a duplicate.
Offer SAML and OIDC to customer IT teams without a separate integration. Domains route to the right connection.
Password, social, SSO, and passwordless all resolve to the same session and token model.
Multi-factor authentication
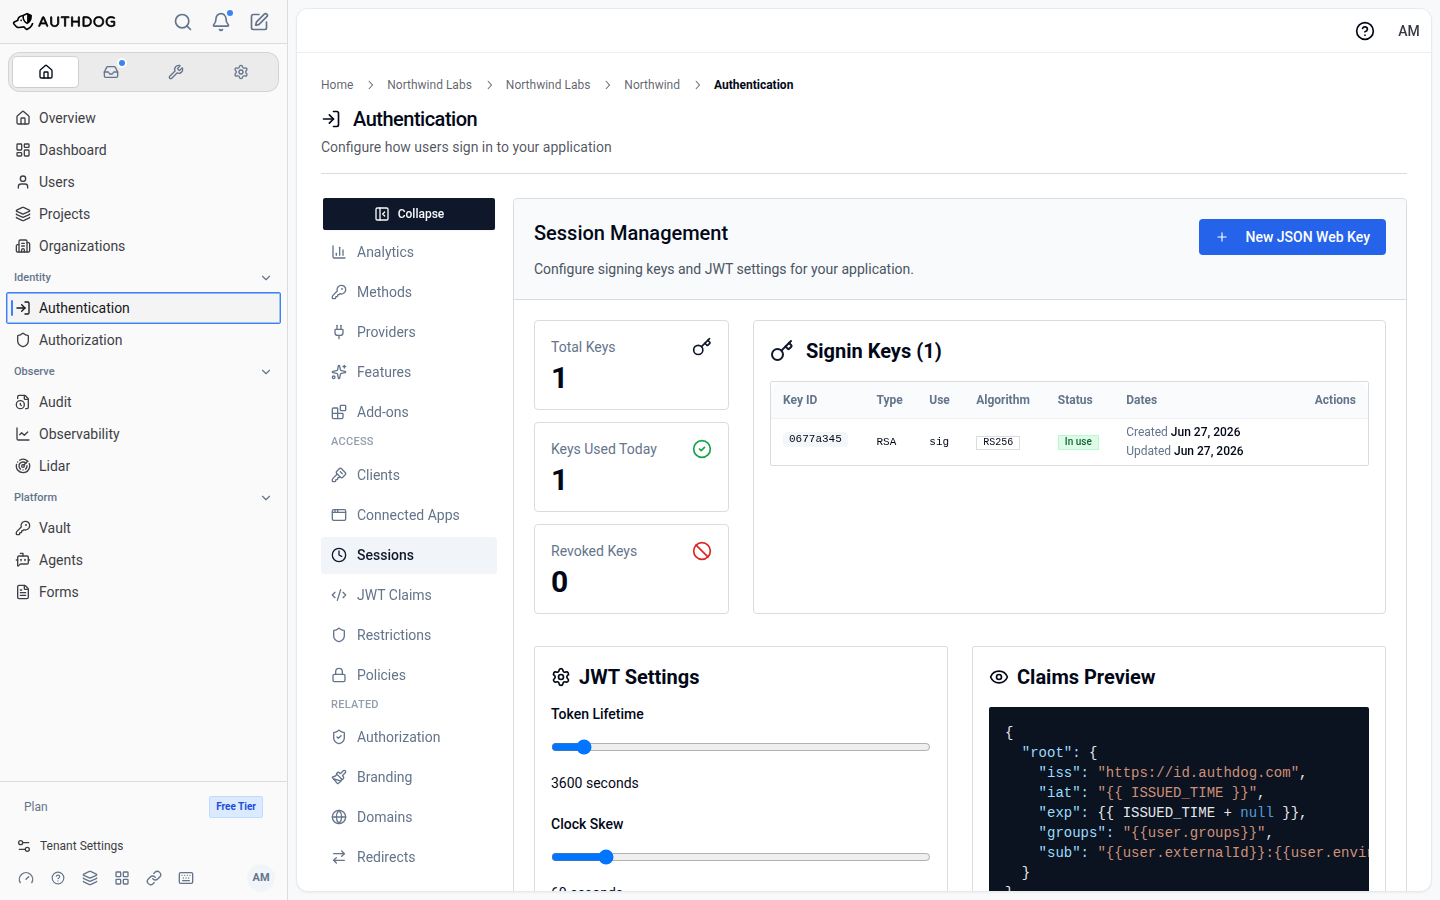
Layer a second factor onto any sign-in method. Enrollment and recovery flows come with it.
One-time codes through your configured messaging and email providers, rate limited and replay protected.
Standards-based TOTP with QR and manual enrollment built into the hosted flows.
FIDO2 and WebAuthn security keys for the phishing-resistant tier enterprise buyers ask about.
One-time recovery codes and admin-assisted reset with an audit trail, so a lost factor is not a lost account.
Passwordless
Eliminate forgotten passwords and credential stuffing. The password stays as a fallback, not the only door.
Platform and cross-device passkeys for phishing-resistant sign-in users never have to remember.
Single-use, expiring sign-in links delivered from your own sending domain.
Short numeric codes for native and TV apps where tapping a link is awkward.
Sign in across platforms with an account users already trust.
Console
Turn methods on, see what happened, and show an auditor later. No deploy required.
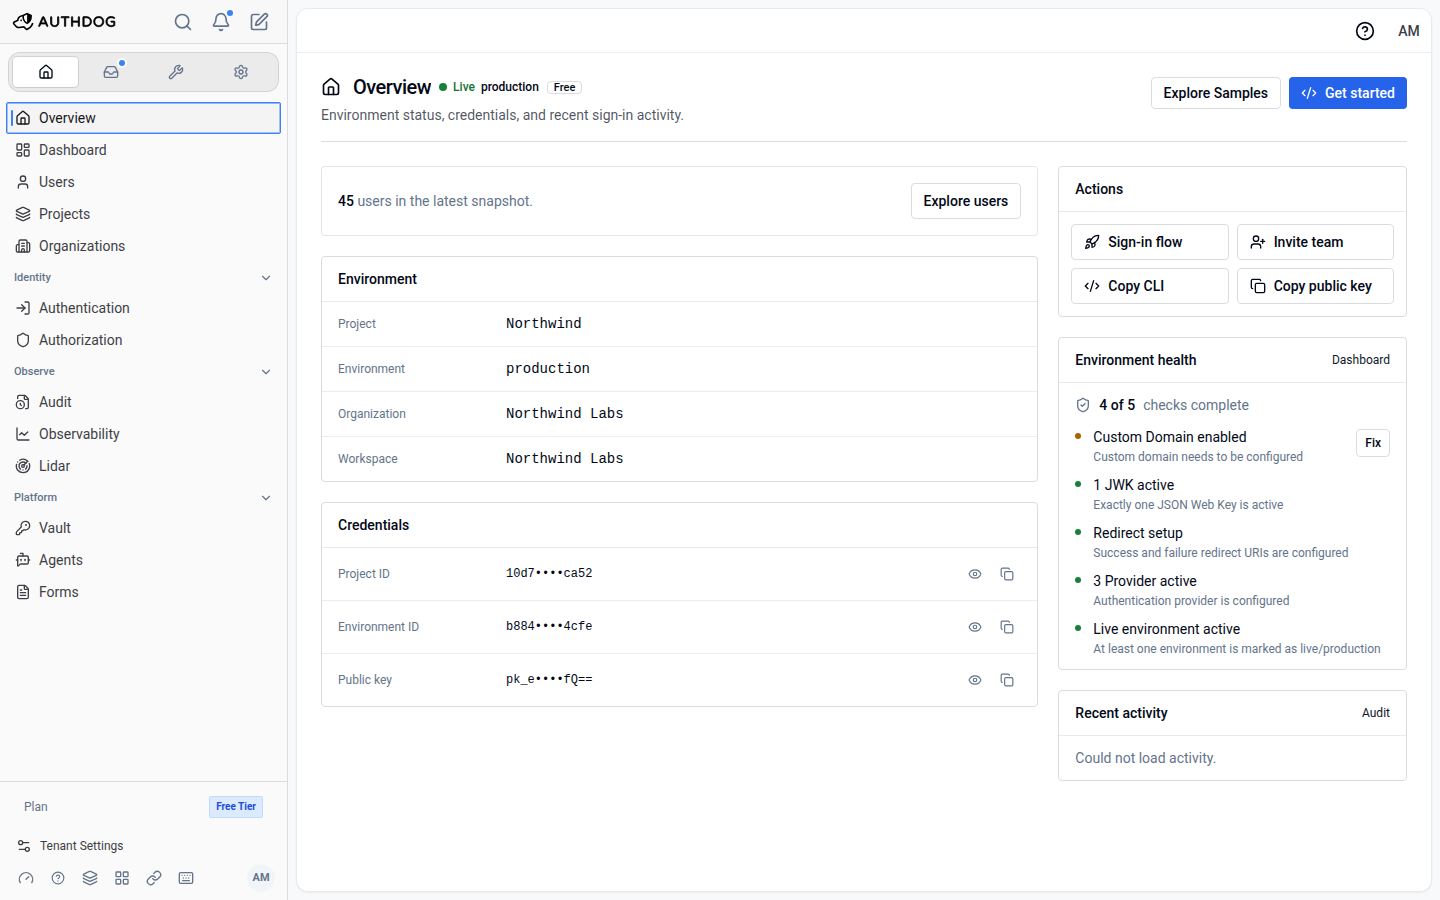
Track sign-ups, activity, and retention
Security, privacy, and compliance
Session lifecycle, breach checks, and brute-force defense ship on by default.
The full lifecycle: start, authenticate while active, terminate on expiry or revocation. Per device, per environment.
SOC 2 Type 2 and ISO 27001 in progress, with regular third-party audits and pen testing.
Custom password policies, with credentials checked against known breach corpora at sign-up.
Suspicious sign-in attempts throttled and flagged automatically, with audit events streamed to your SIEM.
How it works
Connect
Install one SDK or point your app at the hosted sign-in pages.
Configure
Enable the methods, providers, and factors you want per environment.
Ship
Go live with sessions, tokens, and audit logs at the edge.
Build with AI
Ready-made prompts for your favorite AI assistant. Each references real Authdog SDKs, APIs, and documentation.
Claude
Anthropic's AI assistant
Add Authdog authentication to my Next.js app...
ChatGPT
OpenAI's conversational AI
Implement sign-in with social providers...
Cursor
AI-powered code editor
Add MFA/TOTP to existing auth flow...
Free trial
Tell us what you're building and we'll get you set up with a trial, plus someone who can answer questions as you evaluate.
Open the console. Turn on a provider. See a session land.